Quick Answer
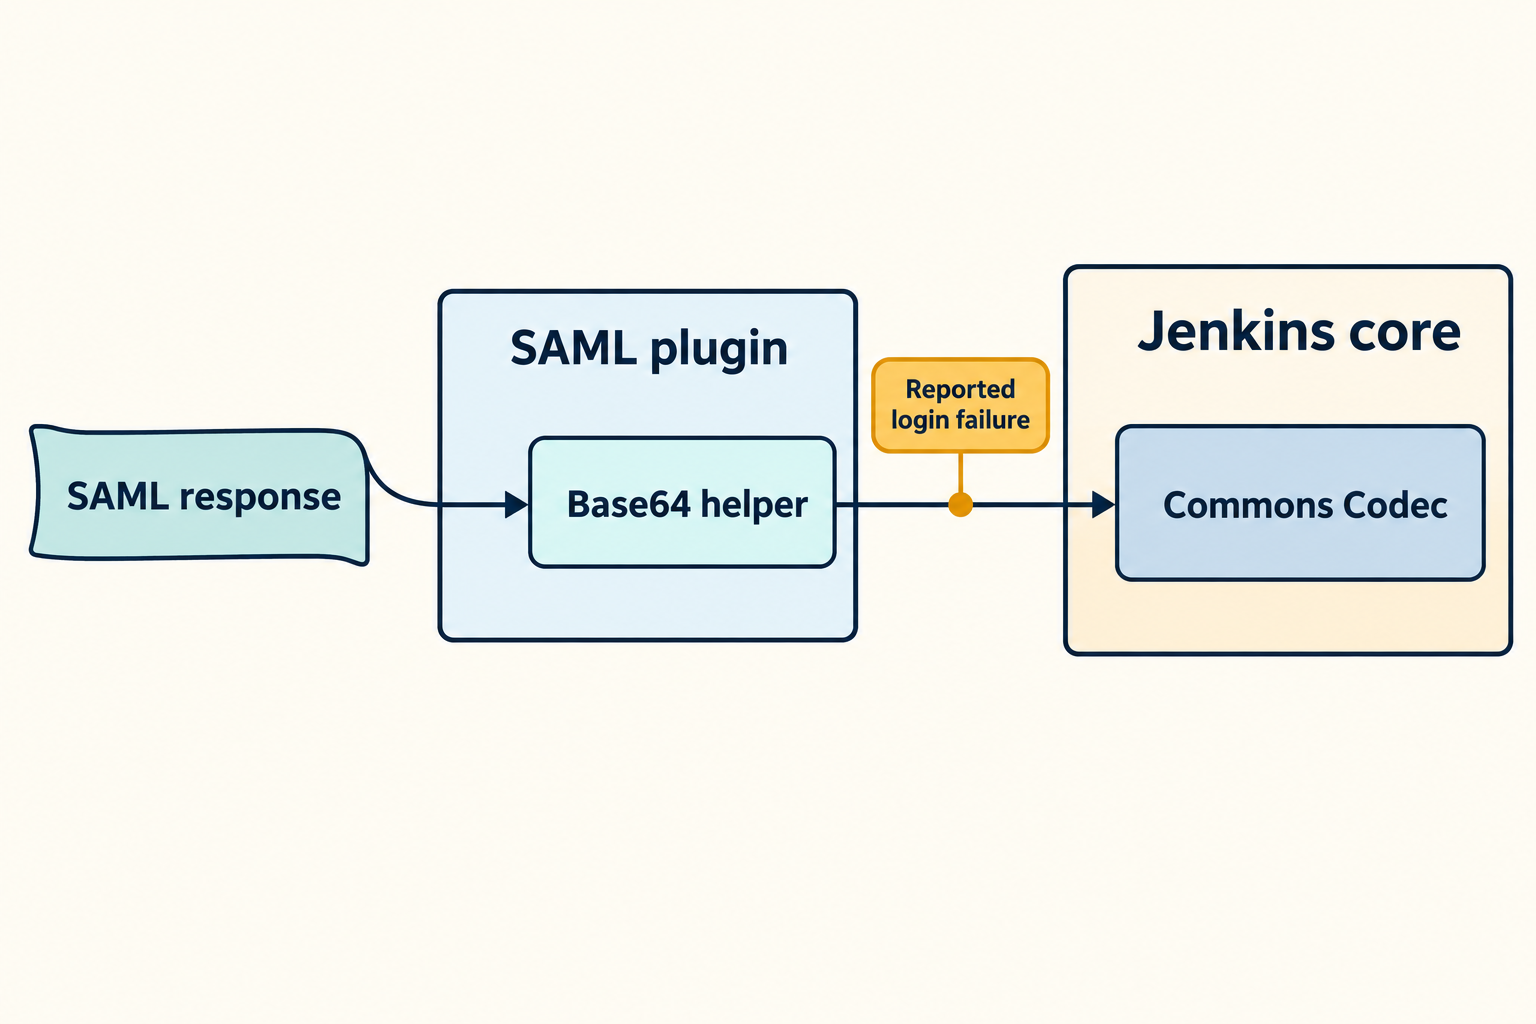
Jenkins 2.587 restores Apache Commons Codec 1.22.1 after the 1.23.0 update was associated with a reported SAML login regression in Jenkins 2.586. The 2.587 changelog, dated October 18, 2026, records the rollback as a released bug fix. The merged change also restricts Renovate to Commons Codec versions below 1.23.0. It restores the earlier dependency; it does not change Jenkins’ SAML decoder implementation.
In Plain English
The reported failure concerns the textual form of a Base64-encoded SAML response. An identity provider can send the encoded response without line breaks, while a decoder can be configured around a particular line length and separator. In the reported setup, those details became consequential after Commons Codec 1.23.0 tightened strict decoding behavior.
According to Jenkins issue #27539, the Shibboleth helper constructed its Base64 decoder with a 76-character line length, LF separators, and CodecPolicy.STRICT. In the reporter’s setup, every login failed at /securityRealm/finishLogin with the exception “Strict decoding: Invalid line separator or line length.” The trace passed through Commons Codec Base64 decoding and the SAML plugin’s POST response decoder.
The Commons Codec release notes describe the underlying library change: version 1.23.0 requires strict Base32 and Base64 decoding to follow the encoder’s canonical alphabet, padding, and line separators, and validates streams through EOF. The notes identify LENIENT as the option for retaining permissive decoding. That documents a library behavior change; it does not establish that every integration using strict decoding is broken.
Code Evidence
The dependency rollback
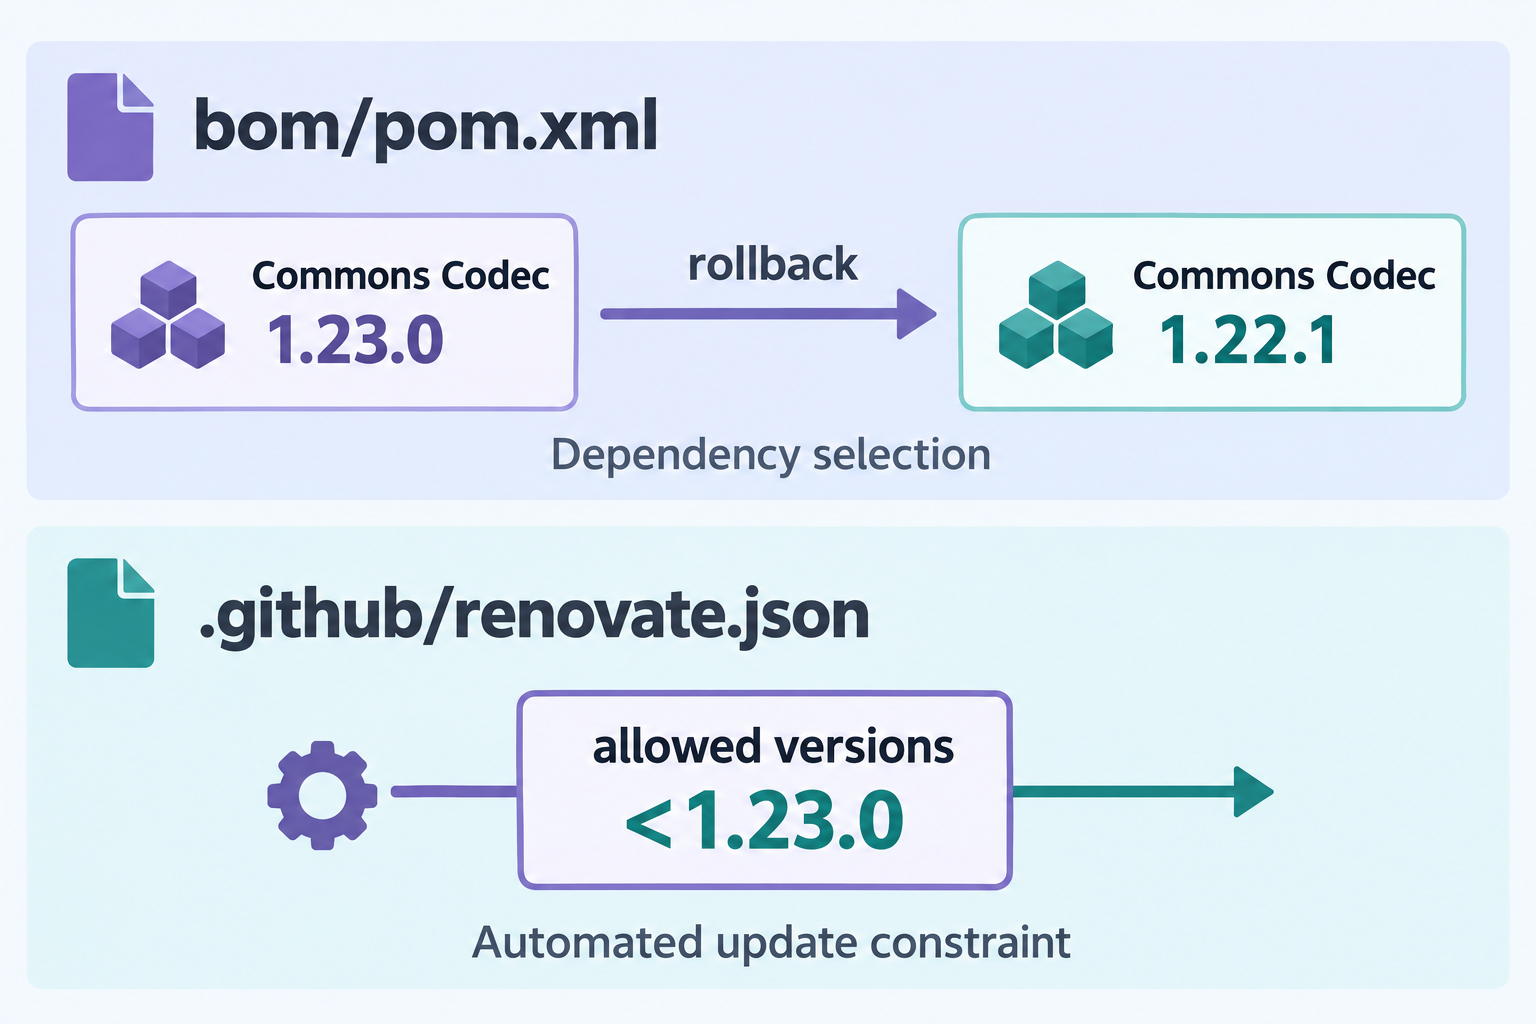
PR #27542 merged into Jenkins master on October 15, 2026. Its merged diff changes the Commons Codec dependency in bom/pom.xml from 1.23.0 to 1.22.1. These are the supplied dependency blocks, shown separately to make the version change explicit.
Before:
<dependency>
  <groupId>commons-codec</groupId>
  <artifactId>commons-codec</artifactId>
  <version>1.23.0</version>
</dependency>
After:
<dependency>
  <groupId>commons-codec</groupId>
  <artifactId>commons-codec</artifactId>
  <version>1.22.1</version>
</dependency>
The second changed file, .github/renovate.json, adds a constraint allowing versions below 1.23.0. These are two distinct controls: the BOM selects the restored dependency, while the Renovate rule constrains subsequent automated update proposals. The supplied evidence supports that rule’s behavior, but does not supply its complete JSON block, so no reconstructed configuration is presented as source code.
The reported reproduction
The issue’s reproduction encodes 300 zero bytes with Java’s Base64 encoder and passes the resulting unwrapped string to Shibboleth’s Base64 helper. The following is an editorial Java illustration of those reported operations, not a verbatim source excerpt or a test executed for this article.
// Editorial illustration of the reported reproduction.
byte[] input = new byte[300];
String encoded = java.util.Base64.getEncoder().encodeToString(input);
net.shibboleth.shared.codec.Base64Support.decode(encoded);
The reporter says this succeeds with Commons Codec 1.22.1 and throws with 1.23.0. The reported comparison is more specific than a general claim that Base64 stopped working: unwrapped input, CRLF-wrapped input, and LF-wrapped input without a final LF failed under 1.23.0. Input with LF every 76 characters and a final LF succeeded. Those are source-reported results, not independently reproduced measurements.
Why It Matters
The issue says Commons Codec was loaded from Jenkins core rather than from the SAML plugin. That connects the host application’s dependency selection to a failure surfacing inside a plugin’s decoder. The observed code change is a core dependency rollback; the reported operational symptom is an interrupted login flow.
Editorial inference: reviewing a shared dependency update requires attention to the consumers that use it across plugin boundaries. A plugin can retain its own version and still encounter different library behavior when its host supplies the implementation. Here, that inference rests on the issue’s account of where Commons Codec was loaded and where the decoding exception occurred.
Editorial inference: protocol integration tests benefit from including the wire representations real peers send. The reported contrast between unwrapped, CRLF-wrapped, and LF-wrapped input suggests a useful compatibility matrix. Testing only the decoder’s preferred line-wrapped representation could miss the input form involved in an actual login exchange. This is a testing recommendation drawn from the report, not evidence that such coverage has been added.
Editorial inference: the Renovate restriction helps preserve the rollback during later dependency maintenance. It does not resolve the compatibility question inside the decoder stack. Restoring a previously working version and determining how to accept a newer version remain separate engineering tasks.
An Open Question
What compatibility change would let Jenkins remove the Commons Codec restriction below 1.23.0: a SAML plugin update that selects lenient decoding, a change to the helper’s line-wrapping configuration, or another upstream adjustment?
The supplied sources do not establish that any of those changes has shipped. Resolving the question would require an identified compatibility change and evidence that the previously failing input representations work with the newer dependency, including the reported SAML login path. The rollback and passed PR checks alone do not answer it.
Scope and Limitations
The detailed failure account comes from one reported environment: Jenkins 2.586 with SAML plugin 4.623.v7875d61cd9f5, bundling shib-support 9.2.1, pac4j-saml 6.4.1, and OpenSAML 5.2.1, with AWS IAM Identity Center as the identity provider. The issue identifies Jenkins 2.583, 2.584, and 2.585 as unaffected. That comparison does not establish that every SAML deployment on 2.586 fails.
The reporter suggested that other plugins using Shibboleth or OpenSAML Base64 helpers might also be affected. The supplied material contains no confirmed inventory of those plugins or deployments. Broader impact therefore remains a reported possibility.
The PR author initially stated that no tests had been added and that the change would rely on ci.jenkins.io. The merged PR page subsequently reported 20 passed checks. Its changed files contain the dependency rollback and Renovate rule, with no dedicated SAML regression test. Those checks must not be described as verification of the complete reported login scenario.
No tests were run for the supplied research or this article. Release availability is supported by the Jenkins 2.587 changelog; successful operation in a particular deployment was not independently verified. The evidence documents a rollback, not a Jenkins-side decoder change or a released upstream Shibboleth fix.
Sources
- Jenkins PR #27542: revert Commons Codec 1.23.0 — merge, testing statements, and reported check count.
- Merged Jenkins commit 2d99bcf828f34d1094c57ac2485cd373fbdd28c9 — dependency rollback and Renovate constraint.
- Jenkins PR #27542 changed files — reviewable diff.
- Jenkins 2.587 changelog — released fix and release date.
- Jenkins issue #27539 — environment, reproduction, exception, and input comparisons.
- Apache Commons Codec release notes — documented strict decoding changes and lenient option.
- Node.js 26.12.1 release notes — alternative considered in the supplied research, not evidence for the Jenkins findings.
- CPython PR #154508 — alternative considered in the supplied research, not evidence for the Jenkins findings.